TL;DR

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
A security researcher has demonstrated a vulnerability in Honda Civic headunits, dubbed ‘Evil Valet,’ which allows attackers with physical access to install malicious updates via USB. This could enable arbitrary code execution and control of the vehicle’s infotainment system.
A security researcher has revealed a vulnerability in Honda Civic headunits that allows attackers with physical access to install malicious updates via USB, potentially gaining control over the vehicle’s infotainment system. This development raises concerns about vehicle security and the risks posed by physical access exploits.
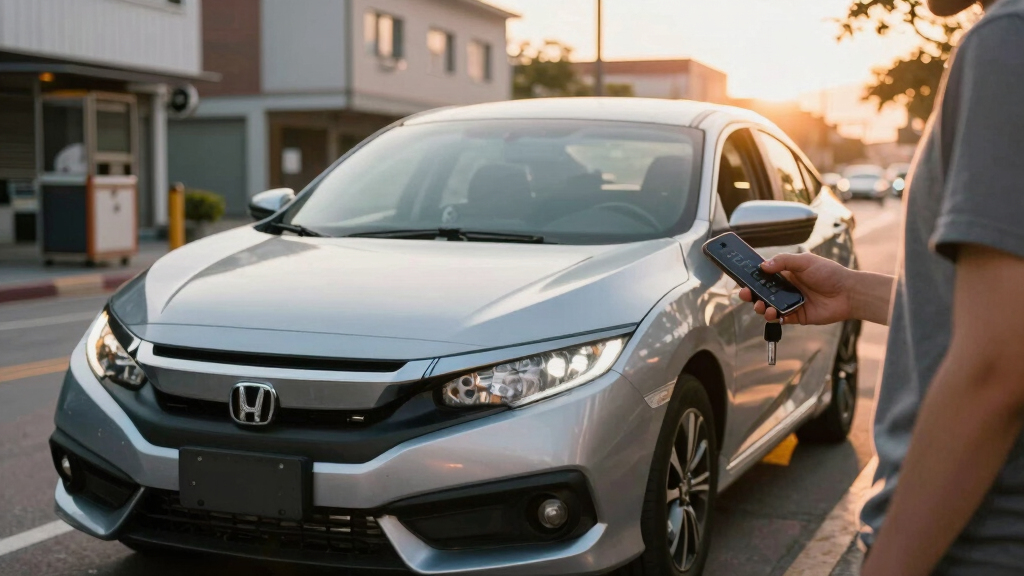
The researcher, who initially reverse-engineered the 2021 Honda Civic headunit, confirmed that the device accepts updates signed with a publicly known AOSP test key. By formatting a USB drive and signing it with this key, an attacker can stage and apply arbitrary updates without needing root access, including malicious code execution. This process, dubbed ‘Evil Valet,’ involves an attacker, such as a valet working for a government agency, installing malicious updates when the vehicle is left unattended.
The researcher developed tools like ‘ota-builder’ to facilitate creating such malicious update files and ‘apk-rebuilder’ to analyze Honda’s update files. While the vulnerability hinges on the headunit’s signing process and update mechanism, it does not require network access or software exploits, only physical access to the car’s USB port. The researcher emphasizes that all updates are likely signed with the test key, making this attack broadly feasible.
Honda has not yet issued a public statement addressing this vulnerability, and it remains unclear whether Honda has implemented mitigation measures or plans to do so. The researcher warns that users should be cautious about leaving their vehicles with untrusted personnel, especially in environments where malicious actors could access the USB port.
Potential Risks to Vehicle Security and Privacy
This vulnerability highlights a significant security risk for Honda Civic owners, especially those who leave their vehicles in public or semi-public spaces. An attacker with physical access could install malicious firmware or software, potentially gaining control over the infotainment system or other vehicle functions. While the attack currently targets the headunit, the implications could extend to broader vehicle security, depending on how deeply integrated the infotainment system is with other vehicle controls. The disclosure underscores the importance of hardware security in modern connected vehicles and raises questions about the safety of update mechanisms relying on signed firmware.
Honda Civic USB firmware update protection
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Honda Civic Headunit Update Mechanics and Security Flaws
The Honda Civic’s headunit supports firmware updates via USB, which are signed with a known AOSP test key. Researchers have confirmed that the update process involves verifying signatures but that the verification logic matches stock AOSP, allowing signing with the test key to bypass security checks. This flaw enables an attacker with physical access to prepare and install malicious updates that are accepted by the system.
Previous work by the researcher involved reverse-engineering the headunit’s update process, developing tools to analyze and reconstruct update files, and demonstrating how to sign custom updates. The vulnerability is not limited to a specific model year but appears to be inherent to the update process used across certain Honda Civic models. Honda has not publicly acknowledged or addressed this issue, and the scope of affected vehicles remains to be fully determined.
“As long as you can properly format a USB drive and sign it with the publicly-known AOSP test key, you can install whatever you want to the headunit, without conventional root access.”
— Researcher
vehicle infotainment system security tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Extent of Vulnerability and Manufacturer Response Unclear
It is not yet confirmed how many Honda Civic models are affected, as the researcher tested specific firmware versions. Honda has not issued a public statement, and it remains unknown whether Honda has implemented security patches or mitigations. The full scope of potential damage and whether other vehicle systems are vulnerable is still under investigation.
As an affiliate, we earn on qualifying purchases.
Honda and Security Community Responses Expected Soon
Honda may release security updates or patches to address this vulnerability. Researchers plan to further analyze the scope of affected vehicles and develop more advanced tools to detect and prevent such exploits. Vehicle owners are advised to be cautious about leaving their cars with untrusted personnel and to monitor official channels for updates.
As an affiliate, we earn on qualifying purchases.
Key Questions
Can this vulnerability be exploited remotely?
No. The attack requires physical access to the vehicle’s USB port, so remote exploitation is not currently feasible.
Does this affect all Honda Civics?
It is not yet confirmed. The vulnerability has been demonstrated on specific firmware versions, but further investigation is ongoing to determine the full scope.
What can owners do to protect their vehicles?
Owners should avoid leaving their cars with untrusted personnel, especially in environments where malicious actors could access the USB port. Monitoring official security advisories from Honda is also recommended.
Will Honda issue a fix?
There has been no official statement yet. It is expected that Honda may release patches or updates once the vulnerability is fully assessed.
Source: Hacker News
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.