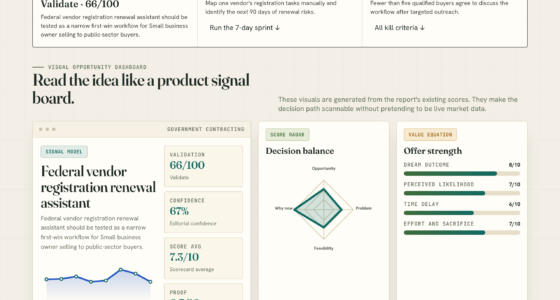
📊 Full opportunity report: Defense Contractor Cybersecurity: Plan For CMMC Compliance on IdeaNavigator AI — validation score, market gap, and execution plan.

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
The material describes a proposed software approach to help small and midsize defense contractors prepare documentation for CMMC Level 2; it does not report a product launch or new government action. The opportunity is framed around the phased rollout that began in November 2025, but market-size, readiness and cost figures are estimates that need independent verification.
IdeaNavigator AI has outlined a proposed readiness workflow for small and midsize U.S. defense contractors seeking CMMC Level 2, centered on self-assessment and preparation of compliance documents. The material describes a business opportunity and an initial product design, not a launched service or a new Department of Defense requirement; its relevance is the phased CMMC rollout that began in November 2025.
The proposed product would guide a contractor through a NIST SP 800-171 assessment, then use the answers to draft a System Security Plan (SSP) and Plan of Action and Milestones (POA&M). It would also calculate an SPRS score, organize evidence against the 110 security requirements, and lay out remediation priorities. The proposal recommends starting with structured assessment and document generation rather than building a full continuous-monitoring system.
The intended users are IT or compliance leads, fractional CISOs and owner-operators at smaller defense contractors and subcontractors that handle Federal Contract Information (FCI) or Controlled Unclassified Information (CUI). IdeaNavigator AI suggests a subscription priced by company size or scope, with possible paid remediation and evidence-collection services. Those prices and add-ons are business-model proposals, not announced product offerings.
To test demand, the proposal suggests running free guided assessments with 15 to 25 contractors, then measuring completion, interest in generated documents and willingness to pay for a pilot. A landing page offering a readiness score and draft SSP is another proposed validation step. No results from such testing, customer commitments or product performance data are provided.
The Cost of CMMC Readiness
The proposal addresses a practical pressure point: a contractor may need to document its security practices and address gaps before it can meet the terms of a relevant DoD solicitation. Smaller firms often have fewer dedicated cybersecurity and compliance staff than large prime contractors, so organizing evidence, policies and remediation work can compete with day-to-day operations. A guided workspace could reduce administrative effort if it produces accurate, usable records.
That potential should not be confused with certification. Software-generated documents do not establish that controls are implemented, nor do they guarantee a passing assessment or eligibility for a contract. Contractors still need to verify their systems, remediate deficiencies and meet the assessment or self-assessment requirements applicable to each solicitation. The value of a tool would depend on how well it reflects the company’s actual environment and stays aligned with the rules in force.
Products Worth Considering

Logitech MX Mechanical Wireless Illuminated Keyboard, Tactile Quiet, Graphite

DJI Mini 3 Drone with DJI RC Controller

Amazon Kindle Scribe Colorsoft 64GB with Premium Pen
As an affiliate, we earn on qualifying purchases.
CMMC Rollout and Contractor Duties
The material says the CMMC DFARS final rule took effect November 10, 2025, beginning a three-year phased rollout. Under that schedule, applicable self-assessment and third-party assessment requirements are expected to appear in selected solicitations during Phase 1 and become broadly mandatory by November 2028. The exact requirement for a contractor depends on the solicitation and the information it handles; the date alone does not mean every contractor must immediately obtain the same assessment.
Level 2 preparation draws on NIST SP 800-171 requirements and calls for documentation, evidence and a plan to address unmet requirements. The proposal estimates first-cycle work can cost $75,000 to more than $300,000 and take 12 to 18 months, and says only about 1% of the Defense Industrial Base is assessment-ready. It also projects more than 118,000 organizations may need Level 2 certification, with about 68% of affected entities being small businesses. These are estimates in the proposal; no underlying study, measurement date or methodology is supplied here, so they should not be treated as verified counts or universal cost and timeline figures.
Demand and Readiness Estimates
No product launch, customer pilot or adoption results are reported. It is not clear whether contractors would pay for the proposed workflow, whether generated SSPs and POA&Ms would meet their needs, or how the tool would be checked against each organization’s real systems. The proposal also does not identify a vendor, development team, security architecture or schedule.
The market and burden figures—including the 1% readiness estimate, projected company count, small-business share, cost range and 12-to-18-month timeline—lack cited methods or dates in the material. They are best read as planning assumptions, not independently confirmed measurements. The specific CMMC level and assessment route required for an individual firm will depend on applicable contract clauses and program rules.
Testing the Readiness Workflow
The next step described is demand validation: invite 15 to 25 small DoD contractors to complete guided NIST SP 800-171 self-assessments, then track whether they finish, value the draft documents and agree to a paid pilot. The proposal also suggests measuring qualified interest through a landing page. No dates or outcomes are given, so it remains unknown whether this testing has begun.
For contractors, the immediate practical step is to review the requirements tied to current and upcoming solicitations, identify the information handled, and assess their own documentation and control gaps. Any readiness software should be treated as an aid to that work, not a substitute for implementation, evidence validation or an assessment when one is required.
Source: IdeaNavigator AI
Key Questions
Is this an announcement of a new CMMC product?
No. The material presents a proposed product concept and ways to test demand; it gives no launch date, vendor details or customer results.
What would the proposed workspace do?
It would guide a NIST SP 800-171 self-assessment and use responses to draft an SSP and POA&M, calculate an SPRS score and organize evidence and remediation priorities. The proposal does not show that these features have been built or independently evaluated.
Does using a readiness tool guarantee CMMC certification?
No. A tool can help organize preparation, but it cannot by itself establish that security requirements are implemented or guarantee a successful assessment or contract eligibility.
When do CMMC requirements apply to contractors?
The described rollout began on November 10, 2025, with requirements phased into selected solicitations and broader application expected by November 2028. A contractor should check the specific clauses and assessment requirements in the contracts it pursues.
Are the cited cost and market figures verified?
The proposal gives estimates for readiness rates, affected businesses, cost and duration, but supplies no methodology or measurement date. They should be treated as unverified planning estimates, not established facts.
Source: IdeaNavigator AI